Fail2ban 全Drop化 (不單單封鎖服務,只要被封IP,所有服務都會被DROP)
先來這加個東西
vi /etc/fail2ban/action.d/iptables-allports.conf
然後在 [Definition] 裏完整的貼上
type = allports actionstart = iptables -N f2b-<name>
iptables -A f2b-<name> -j RETURN
iptables -I INPUT -p tcp -j f2b-<name>
iptables -I INPUT -p udp -j f2b-<name>
iptables -I INPUT -p icmp -j f2b-<name>
actionstop = iptables -D INPUT -p tcp -j f2b-<name>
iptables -D INPUT -p udp -j f2b-<name>
iptables -D INPUT -p icmp -j f2b-<name>
iptables -F f2b-<name>
iptables -X f2b-<name>
actioncheck = iptables -n --list-chain f2b-<name> || exit 1
actionban = iptables -I f2b-<name> 1 -s <ip> -j DROP
actionunban = iptables -D f2b-<name> -s <ip> -j DROP
[Init]
就可以 systemctl restart fail2ban了
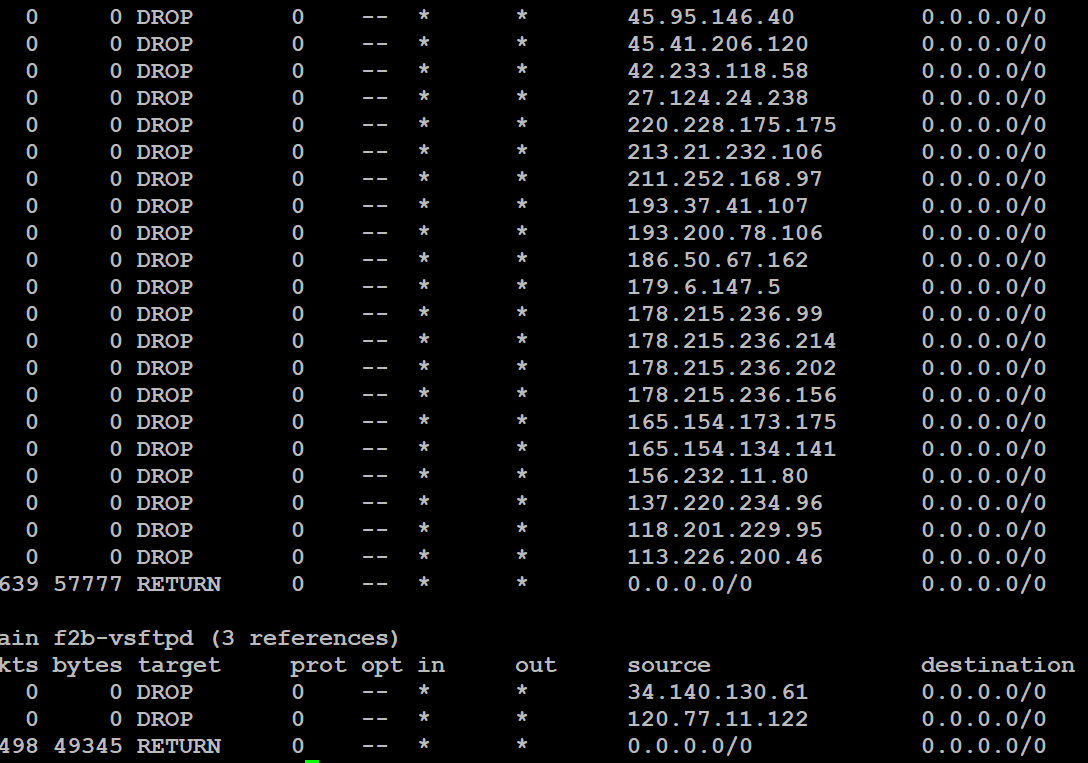
觀察看看iptables
iptables -L -n -v
EX:
jail.local
EX:
[DEFAULT]
ignoreip = 127.0.0.1/8 192.168.1.0/24 jyan-tech.com junlin.com.tw
bantime = 100d
findtime = 30d
maxretry = 3
chain = INPUT #KEY RIGHT CHAIN WHAT YOUR DEVICE
[ssh-iptables]
enabled = true
filter = sshd
action = iptables-allports[name=SSH, port=65477, protocol=tcp]
sendmail-whois[name=SSH, dest=root, sender=seven@jyan-tech.com, sendername="Fail2Ban"]
logpath = /var/log/secure
maxretry = 3
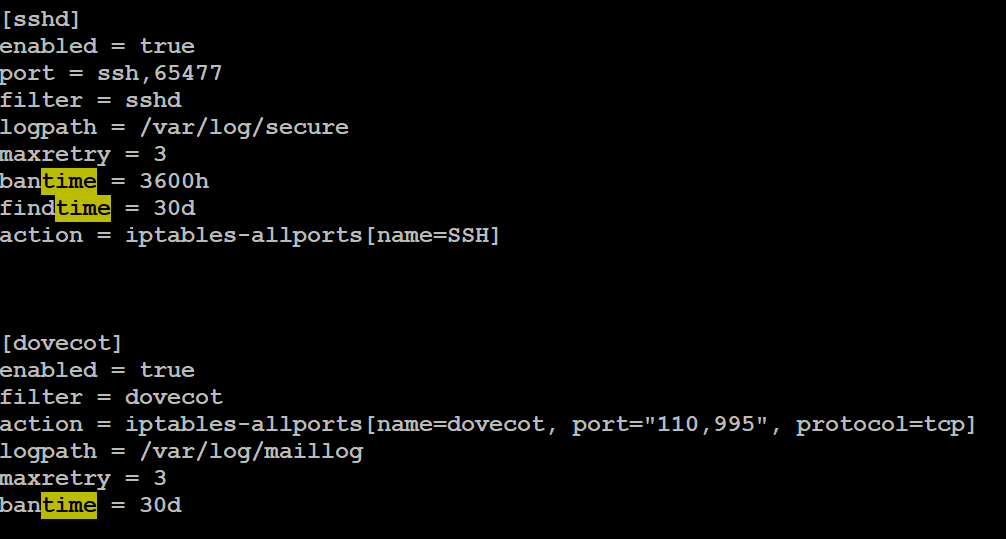
[sshd]
enabled = true
port = ssh,65477
filter = sshd
logpath = /var/log/secure
maxretry = 3
bantime = 3600h
findtime = 30d
action = iptables-allports[name=SSH]
[dovecot]
enabled = true
filter = dovecot
action = iptables-allports[name=dovecot, port="110,995", protocol=tcp]
logpath = /var/log/maillog
maxretry = 3
bantime = 30d
....
....
....